We have noticed that you are using an ad-blocking software
Liveuamap is editorially independent, we don't receive funding from commercial networks, governments or other entities. Our only source of our revenues is advertising.
We respect your choice to block banners, but without them we cannot fund our operation and bring you valuable independent news. Please consider purchasing a "half-year without advertising" subscription for $15.99. Thank you.
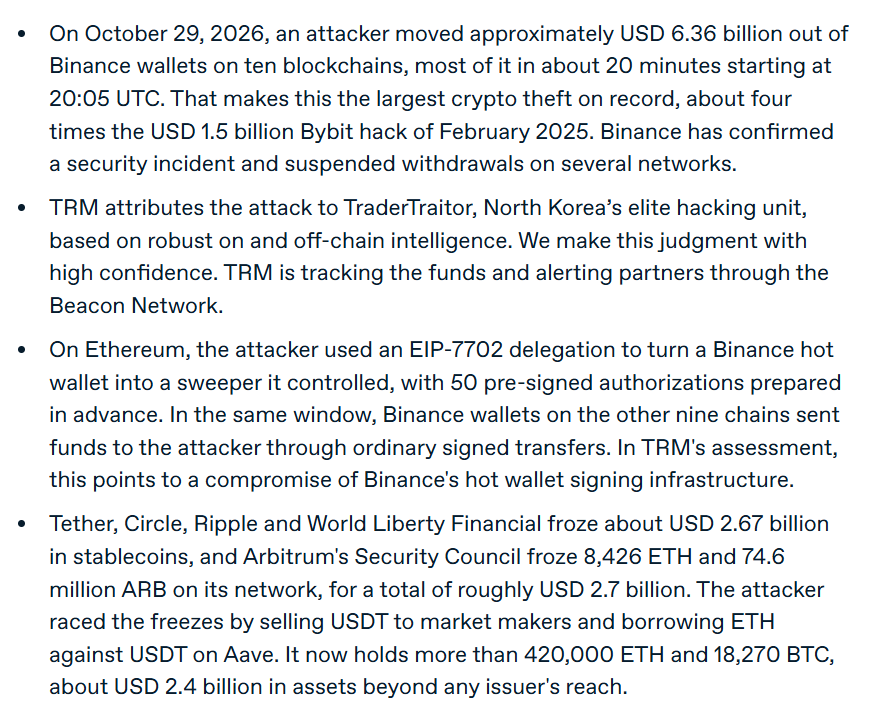
Binance issues statement following suspected crypto hack. "Our teams are aware of reports of a potential security issue and are actively investigating. At this stage, we have not confirmed any impact to user funds. Our security teams are reviewing all relevant information with urgency, and we will provide updates through official Binance channels as soon as we have verified information
Yhdysvaltain oikeusministeriön (DOJ) kansallinen petosvastatoimisto on julkistanut "Ghostbusters"-nimisen operaation, jossa syytetään laajamittaista "petollisen opiskelijan" huijausverkostoa, joka on sidoksissa kenialaiseen verkostoon. Rikolliset ovat varastaneet amerikkalaisten henkilöiden henkilöllisyyksiä, jotka eivät ole käyneet yliopistoja, lähettäneet vääriä FAFSA-hakemuksia, rekisteröineet "petollisia" opiskelijoita ja ohjanneet jäljellä olevia liittovaltion avustusvaroja ulkomaille, kun yliopistot ovat ottaneet oman osuutensa. Viisi henkilöä on jo syytetty, yli 750 000 dollaria kryptovaluuttaa on takavarikossa, ja tiimi on nyt paikalla Keniassa. Toiminta on aloitettu vuonna 2021, ja se on todennäköisesti aiheuttanut veronmaksajille satoja miljoonia dollareita, samalla estäen avustusta oikeille opiskelijoille.
Pentagon epäilee, että kyberhyökkäys on aiheuttanut useita jääkaappien toimintahäiriöitä, jotka ovat pilaanneet ruokaa Yhdysvaltain armeijan tukikohdissa ympäri maata elokuussa, Reuters raportoi, viitaten neljään tiedonlähteeseen.
PHP2Shell käytössä todellisissa hyökkäyksissä. Hyökkääjä yhdisti PHP2Shellin Linux-ydinvirheen avulla, jolloin hän sai pääsyn 25 palvelimeen neljässä maassa, mukaan lukien kolme Yhdysvaltain hallituksen alaisuudessa olevaan ympäristöön. Hyökkäys ulottui sisäiseen verkkoon, jossa hyökkääjä pyrki hyödyntämään Active Directoryä. Epäillään Kiinan yhteyksiä. Merkkejä tekoälyyn perustuvasta työkalusta.
Hakkeri yrittää murtautua Yhdysvaltain liittovaltion vaalilautakunnan järjestelmiin, ja kyseinen toimiala on joutunut "väliaikaisesti sulkemaan" verkkopalvelunsa, Reutersin toimittajalle lähetetyn sähköpostin perusteella.
Trump: Lyhyellä aikavälillä, me olemme virallisesti KÄSKÄMÄÄN käyttää termiä "AI/Artificial Intelligence" kaikissa asiaankuuluvissa asiakirjoissa ja muissa yhteyksissä, sen epätarkkuuden vuoksi.
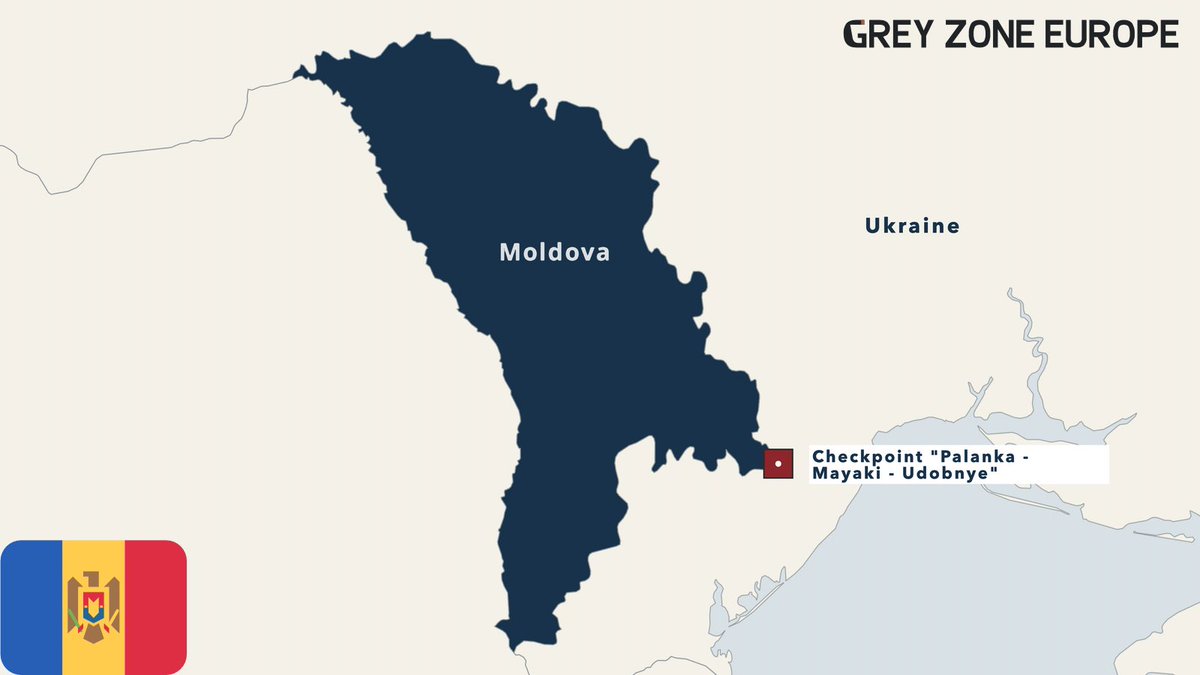
Moldovan hallituksen digipalvelut edelleen häiriöillä, suurikokoinen kyberhyökkäys aiheutti vahinkoa. Viranomaiset rekisteröivät noin 11 MILJONIA pyyntöä 22. lokakuuta, kun hyökkäys kohdistui henkilötietoihin. Toinen yritys murtautua estettiin 25. lokakuuta. Useat hallituksen alustat ovat edelleen käytöstä poistettu, mukaan lukien järjestelmät, jotka käsittelevät lupia ja virallisia valtuuksia. Moldovan viranomaiset epäilevät, että hyökkäykset voivat olla osa laajempaa hybridioperaatiota. Syyllisyyttä ei ole vahvistettu.
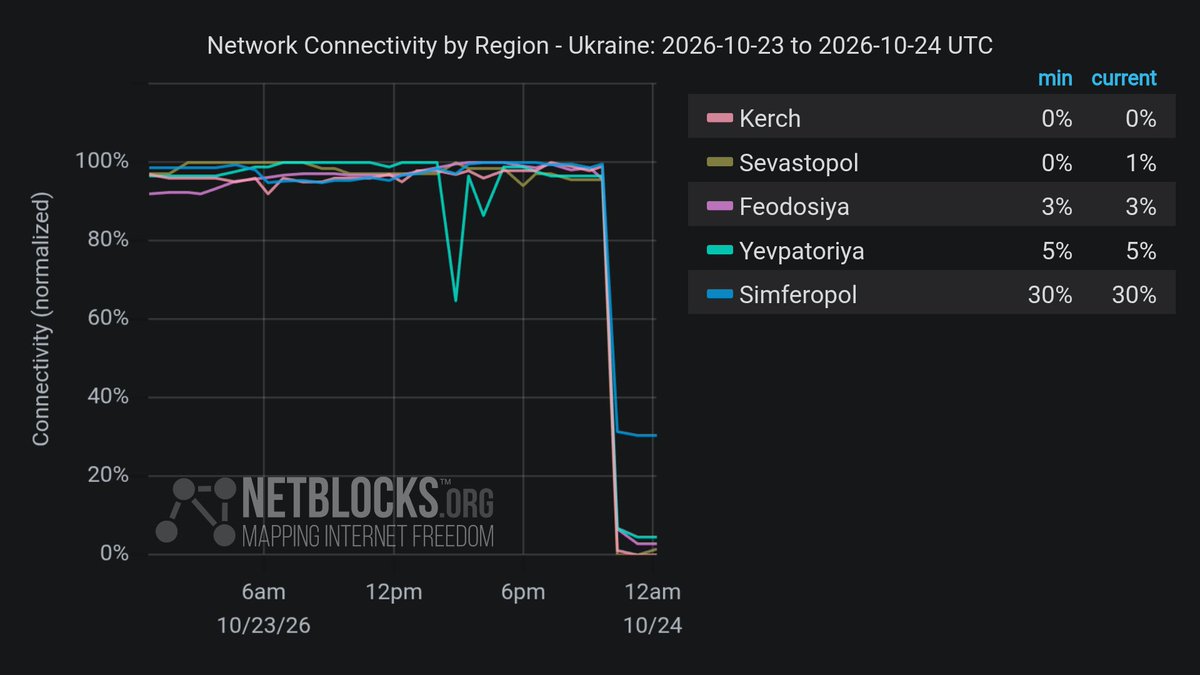
Vahvistettu: Verkkodata osoittavat, että internet-yhteys on katkennut miehitetyllä Krimillä, samalla kun energia-infrastruktuuria kohdistaneet ukrainalaiset droonihyökkäykset ovat aiheuttaneet sähkökatkoja.
After PHP2Shell comes Node2Shell, a critical bug found by OpenAI's Codex Security that can let attackers run code in Node.js apps. It was successfuly demonstrated on the official Node.js 24.22.0 image. Node 20, 23 and 25 (all EoL) get no fix
Venäläiset kalastusalukset epäiltyjä valvomaan kriittisiä merialueen viestintäkaapeleita, jotka yhdistävät Britannian, Euroopan ja Yhdysvallat. Yli 500 epäilyttävää liikettä, joihin on osallistunut 17 alusta, on havaittu, ja alukset ovat toistuvasti hidastaneet, muuttaneet suuntaa ja noudattaneet kaapeleiden reittejä. Brittiläiset viranomaiset pelkäävät, että tämä toiminta voisi auttaa Moskovaa tunnistamaan kohteita tuleville sabotaattitoimille.
Oracle published a security alert for Java today: CVE-2026-91403, CVSS 9.1. It's in JSSE (Java's TLS) and is exploitable over the network without credentials. Affected versions listed: Java SE 8u511, 11.0.33, 17.0.21, 21.0.13, 25.0.5 and 27.0.1, and GraalVM
CRITICAL: GitLab flaw (CVSS 10.0) affects 12 years of releases. CVE-2026-110264 could allow unauthenticated remote code execution on self-managed servers
Microsoft: The China state-aligned threat actor Storm-0940 used the agentic AI penetration testing framework ARTEX to automate attacks targeting hundreds of organizations globally across a broad range of industries. Microsoft Threat Intelligence assesses that Storm-0940 was responsible for the recently disclosed ConnectWise supply chain compromise of a multitenant application. Our investigation found that Storm-0940's use of ARTEX accelerated the speed of compromised application abuse to authenticate to target environments through applications that had already been granted access, allowing the threat actor to operate without requiring an interactive user sign-in. AI-accelerated follow-on activity included reconnaissance, application credential changes, and attempts to modify privileges that could enable expanded or persistent access. Read our blog for a detailed analysis and indicators of compromise (IOCs), along with Microsoft Defender detections, protection recommendations, and guidance on investigating service principal sign-ins and unexpected application credential or privilege changes
Confirmed: Network data show an ongoing disruption to North Korea's already limited internet connectivity. The incident corresponds with the loss of international access to websites under the country's .kp domain
NSA Cyber: Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance
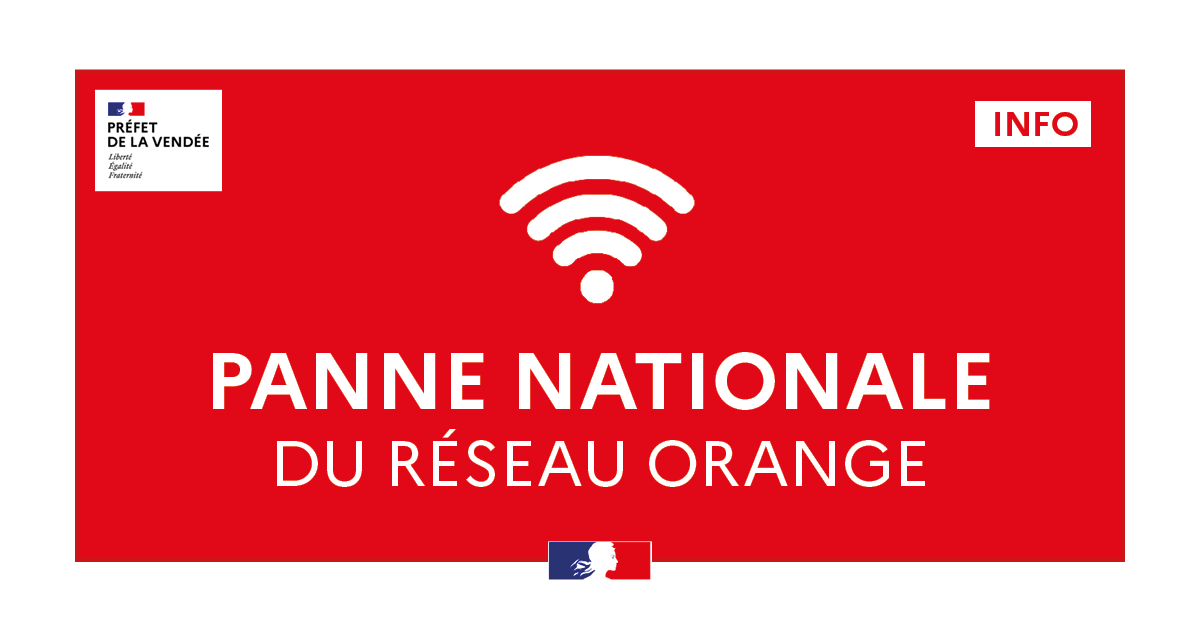
Orange Network Outage: A national outage is affecting Orange and Sosh mobile and internet networks since late morning this Wednesday, October 21. Emergency numbers may be difficult to reach, particularly 15 (SAMU), 17 (police and gendarmerie), and 18 (firefighters). In case of emergency, if your call does not go through, dial 112 from another available mobile network or use a landline
Security firm Calif appears to have a working exploit for the leaked PHP flaws, hours before the patch. A briefly posted video credited to Calif shows it running commands on a WordPress 7.1.3 site on PHP 8.5.4. Kevin Beaumont says a screenshot from it is real. A separate public PoC is also circulating, but its own author now says one of its attack chains is dead and code execution is unreliable. Admins have two stopgaps until the fix lands at 14:00 UTC today. Turning off session.upload_progress.enabled in php.ini disables the feature the leaked details point to. The only cost is upload progress bars. Blocking every request with a multipart Content-Type at the web server goes further, but breaks file uploads
The NCSC is encouraging UK organisations to prepare for immediate updating of systems using PHP. Where immediate remediation is not feasible, organisations should consider taking the system offline until it can be fully mitigated
Widespread internet disruption reported across North Korea. More than 40 websites, including KCNA, Rodong Sinmun and government portals, have experienced significant outages. Network monitors also detected disruptions to Pyongyang's internet infrastructure
The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2. PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence
Multiple online services are down or experiencing issues. Google Cloud has reported "issues" in its western Europe region, affecting dozens of websites, including Revolut, Royal Mail and HSBC
Google Cloud has reported an "issue" affecting dozens of services across the UK They include Revolut, Lloyds, HSBC, Halifax, Rightmove, Royal Mail, Bank of Scotland, DPD and Sky
One week before Serbia's crucial elections, it's confirmed: Belgrade University's rector was hacked with zero-click Pegasus — and a key prosecutor, pulled off a case after speaking out about political interference, got a spyware alert. 16 confirmed targets and counting
Liveuamap.com on Map&Feed Uutiset alusta. Meidän tehtävämme on kertoa
kriisin Ukrainassa ympäri maailmaa. Voimme kerätä tietoja avoimista lähteistä ja laita se kartan muodossa Reds-vs-Blues ristiriita.
Jos haluat jakaa meidän tehtävämme, tai on jokin kysymys, vain sähköposti [email protected] tai kysyä Twitterissä @liveuamap
 UkrainaVenäjä laukaisi yön aikana useita Iskander-M-, Tsirkon-, KN-23- ja S-400-tyyppisiä ballistisia ohjuksia sekä 172 erityyppistä hyökkäysdroonia, Ukrainan ilmavoimat ilmoitti.
 UkrainaYksi kuollut, 13 haavoittunutta, kun venäläiset hyökkäykset Sumyn alueella eilen
 TexasCrash in El Paso's Lower Valley, the El Paso Police Department's Special Traffic Investigation unit was dispatched to another crash involving serious injuries
 South-East AsiaYhdysvaltain lentotukialus "Theodore Roosevelt" saapui Singapuren Changi-laivastotukikohdalle aamulla viralliseen vierailuun. Alus on odotettavissa pysyvän Singaporessa useita päiviä ennen siirtymistä Lähi-itään.
 TexasSouth Gessner officers are at 6200 Gulfton. Three male stabbing victims transported in stable condition. One possible suspect detained
 New YorkWoman fatally stabbed and found naked inside NYC massage parlor: sources
 Kalifornia1 killed in south Sacramento crash that left 2 vehicles overturned
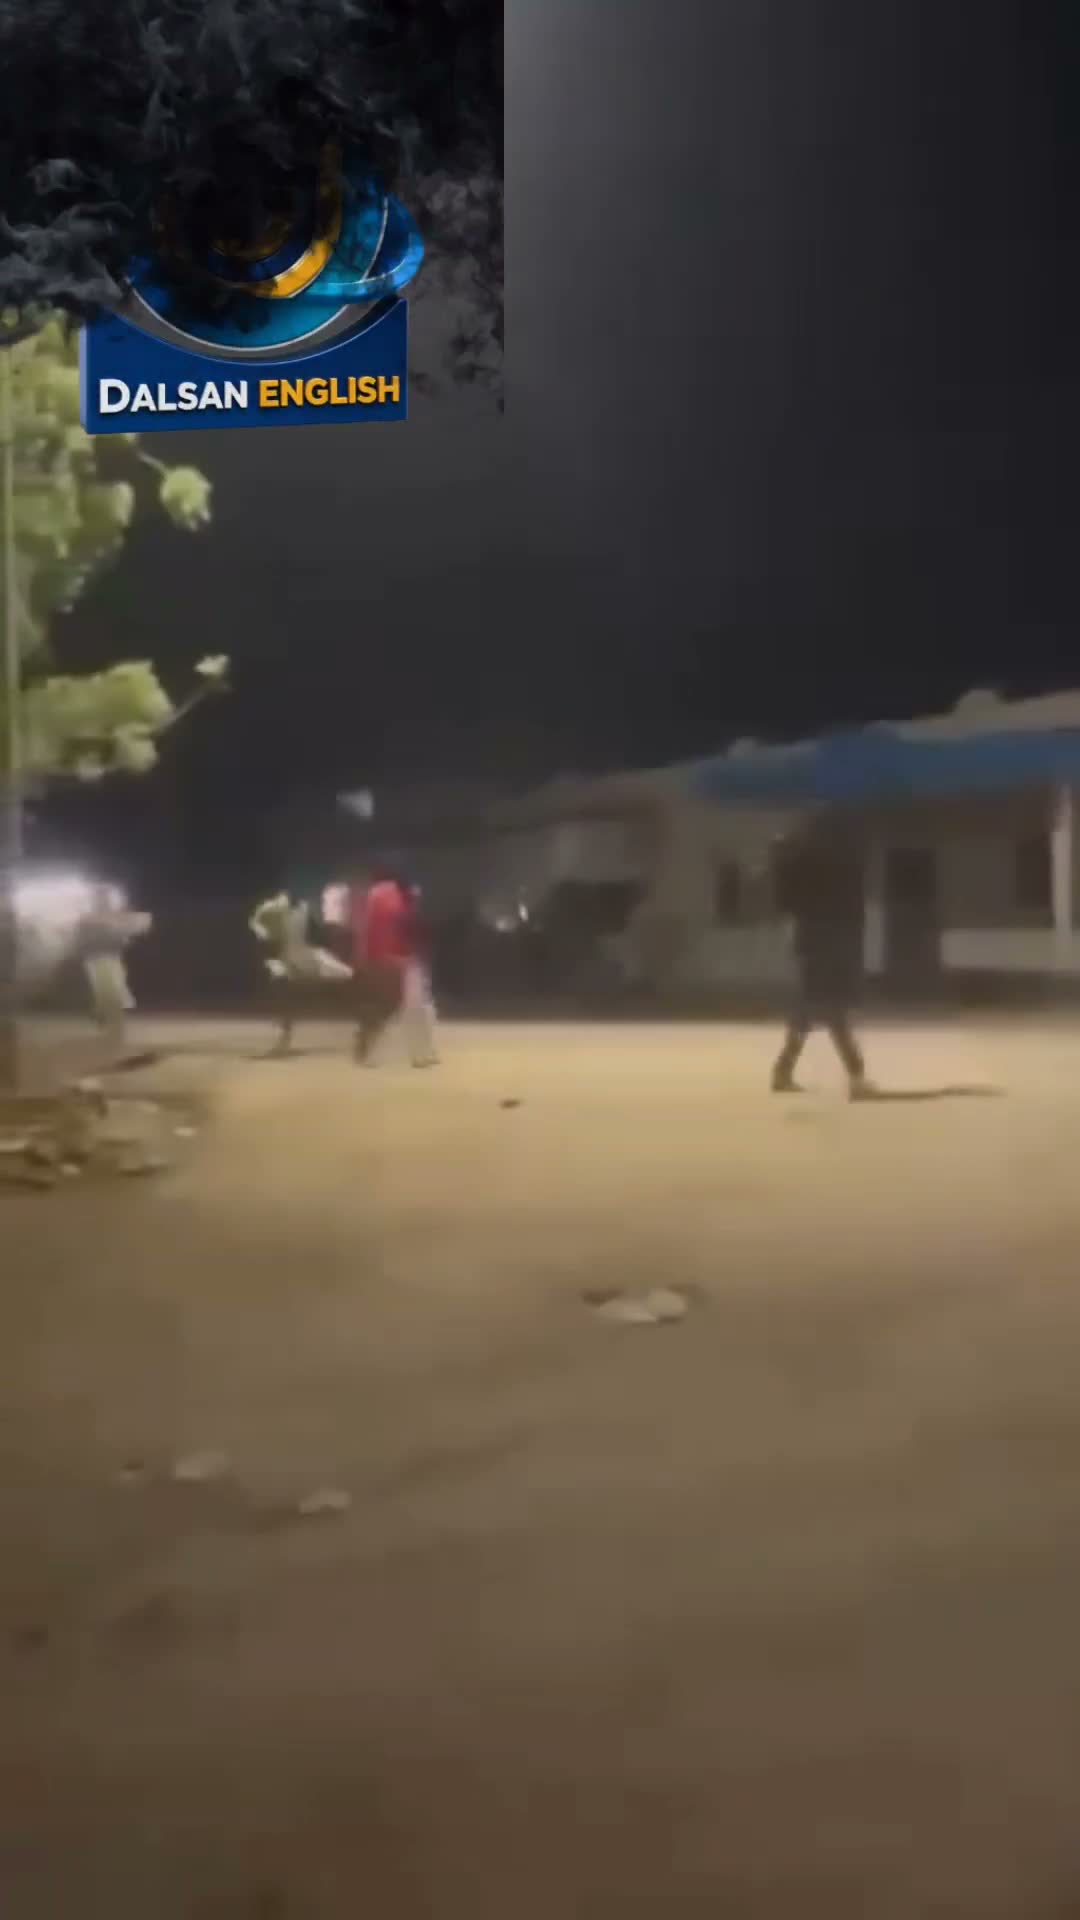 SomaliaTensions are soaring in Beledweyne tonight as heavily armed Macawisley fighters mobilize across the city, sparking fears of an imminent armed clash. The sudden mobilization follows the secretive arrival of a rival Hirshabelle administration deputy leader, who reportedly slipped
 ColoradoDenver Police Arrest Suspect in 2024 Shooting