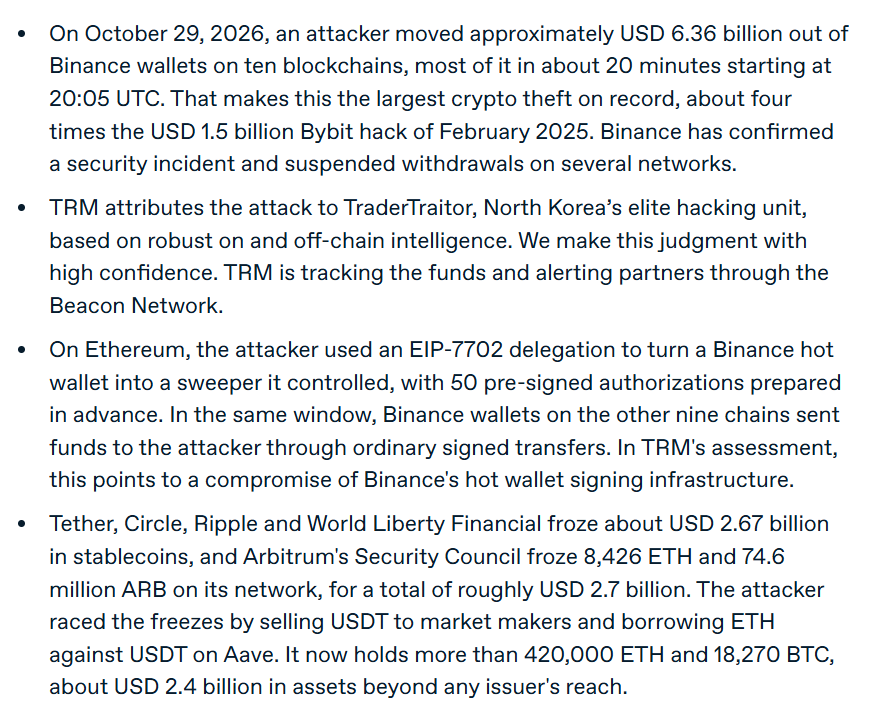
Binance issues statement following suspected crypto hack. "Our teams are aware of reports of a potential security issue and are actively investigating. At this stage, we have not confirmed any impact to user funds. Our security teams are reviewing all relevant information with urgency, and we will provide updates through official Binance channels as soon as we have verified information
We have noticed that you are using an ad-blocking software
Liveuamap is editorially independent, we don't receive funding from commercial networks, governments or other entities. Our only source of our revenues is advertising.
We respect your choice to block banners, but without them we cannot fund our operation and bring you valuable independent news. Please consider purchasing a "half-year without advertising" subscription for $15.99. Thank you.
Binance issues statement following suspected crypto hack. "Our teams are aware of reports of a potential security issue and are actively investigating. At this stage, we have not confirmed any impact to user funds. Our security teams are reviewing all relevant information with urgency, and we will provide updates through official Binance channels as soon as we have verified information
USA:s justitiedepartement (DOJ) National Fraud Enforcement Division har nyligen meddelat anklagelser i Operation Ghostbusters, som riktar sig mot ett landsomfattande "spöstudent"-bedrägeri kopplat till ett kenyiskt nätverk. Brottslingar har stulit identiteter från amerikaner som aldrig studerat på universitet, lämnat in falska FAFSA-ansökningar, registrerat "spöstudenter" och omdirigerat återstående federala bidrag till utlandet efter att universitet tagit sin andel. Fem personer har hittills anklagats, över 750 000 USD i kryptovaluta har beslagtagits och ett team är nu på plats i Kenya. Bedrägeriet, som startade 2021, har sannolikt kostat skattebetalare hundratals miljoner samtidigt som det har blockerat bidrag till riktiga studenter.
Pentagon misstänker att en cyberattack kan ligga bakom en rad problem med frysar som ledde till att mat förstördes på amerikanska militärbaser i augusti, rapporterar Reuters, med hänvisning till fyra tjänstemän som är bekanta med ärendet.
PHP2Shell utnyttjas i verkliga attacker. En angripare kombinerade PHP2Shell med en Linux-kärnfel för att få root-åtkomst till 25 servrar i fyra länder, inklusive tre i en miljö kopplad till den amerikanska regeringen. Intrusionen sträckte sig in i det interna nätverket, där angriparen riktade in sig på Active Directory. Misstänkt koppling till Kina. Tecken på AI-assisterad verktyg.
En hacker försöker komma åt systemen för USAs federala valkommission, och myndigheten har tvingats "tillfälligt stänga av" sina webbtjänster som ett resultat, enligt ett e-postmeddelande som Reuters har tagit del av.
Trump: Vi kommer inom kort att officiellt förbjuda användningen av termen "AI/Artificiell intelligens" i alla relevanta dokument och annat, på grund av dess brist på precision.
Moldavias regering har fortsatt problem med digitala tjänster efter en omfattande cyberattack. Myndigheterna rapporterar om cirka 11 MILJONER förfrågningar under en attack som riktade sig mot personuppgifter den 22 oktober. Ett andra försök till intrång stoppades den 25 oktober. Flera statliga plattformar är fortfarande otillgängliga, inklusive system för att hantera tillstånd och officiella auktorisationer. Moldaviska myndigheter misstänker att attackerna kan vara en del av en bredare hybridkampanj. Tillskrivningen är ännu inte bekräftad.
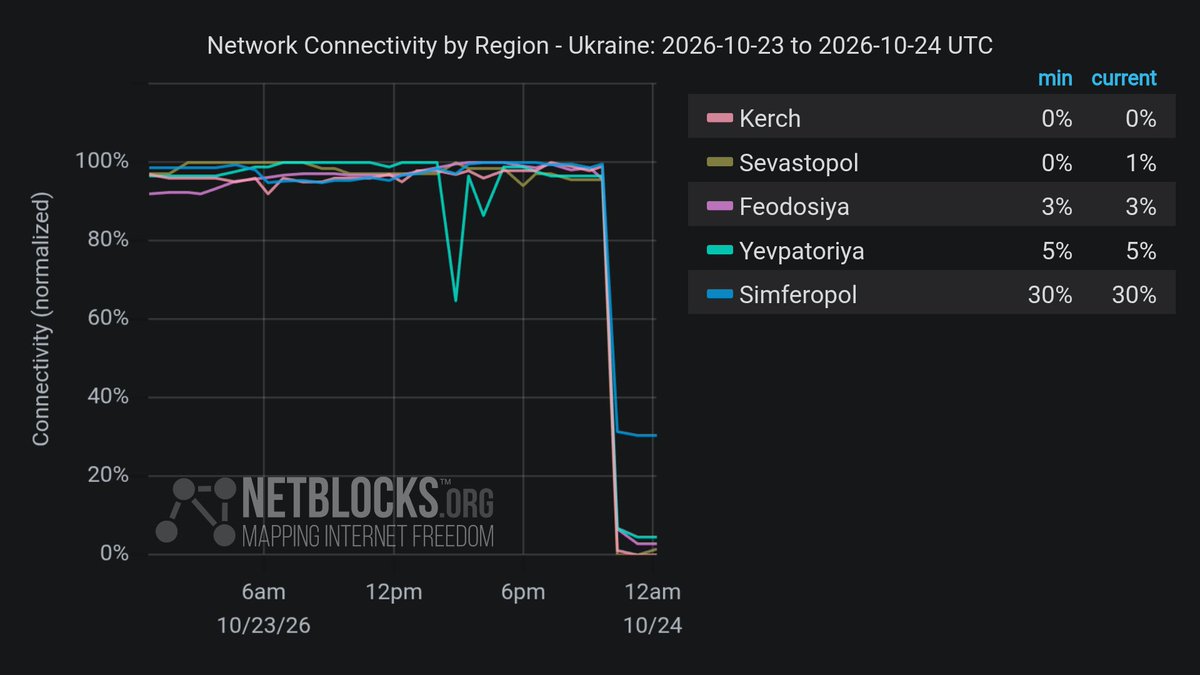
Bekräftat: Nätverksdata visar att internetanslutningen har avbrutits i ockuperade Krim, i samband med strömavbrott efter ukrainska drönattacker mot energianläggningar.
After PHP2Shell comes Node2Shell, a critical bug found by OpenAI's Codex Security that can let attackers run code in Node.js apps. It was successfuly demonstrated on the official Node.js 24.22.0 image. Node 20, 23 and 25 (all EoL) get no fix
Ryska fiskefartyg misstänks för att övervaka viktiga undervattenskommunikationskablar som förbinder Storbritannien med Europa och USA. Över 500 misstänkta rörelser involverande 17 fartyg har identifierats, där fartygen upprepade gånger saktar ner, ändrar kurs och följer kablarnas rutter. Brittiska tjänstemän fruktar att denna aktivitet kan hjälpa Moskva att identifiera mål för framtida sabotage.
Oracle published a security alert for Java today: CVE-2026-91403, CVSS 9.1. It's in JSSE (Java's TLS) and is exploitable over the network without credentials. Affected versions listed: Java SE 8u511, 11.0.33, 17.0.21, 21.0.13, 25.0.5 and 27.0.1, and GraalVM
CRITICAL: GitLab flaw (CVSS 10.0) affects 12 years of releases. CVE-2026-110264 could allow unauthenticated remote code execution on self-managed servers
Microsoft: The China state-aligned threat actor Storm-0940 used the agentic AI penetration testing framework ARTEX to automate attacks targeting hundreds of organizations globally across a broad range of industries. Microsoft Threat Intelligence assesses that Storm-0940 was responsible for the recently disclosed ConnectWise supply chain compromise of a multitenant application. Our investigation found that Storm-0940's use of ARTEX accelerated the speed of compromised application abuse to authenticate to target environments through applications that had already been granted access, allowing the threat actor to operate without requiring an interactive user sign-in. AI-accelerated follow-on activity included reconnaissance, application credential changes, and attempts to modify privileges that could enable expanded or persistent access. Read our blog for a detailed analysis and indicators of compromise (IOCs), along with Microsoft Defender detections, protection recommendations, and guidance on investigating service principal sign-ins and unexpected application credential or privilege changes
Confirmed: Network data show an ongoing disruption to North Korea's already limited internet connectivity. The incident corresponds with the loss of international access to websites under the country's .kp domain
NSA Cyber: Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance
Orange Network Outage: A national outage is affecting Orange and Sosh mobile and internet networks since late morning this Wednesday, October 21. Emergency numbers may be difficult to reach, particularly 15 (SAMU), 17 (police and gendarmerie), and 18 (firefighters). In case of emergency, if your call does not go through, dial 112 from another available mobile network or use a landline
Security firm Calif appears to have a working exploit for the leaked PHP flaws, hours before the patch. A briefly posted video credited to Calif shows it running commands on a WordPress 7.1.3 site on PHP 8.5.4. Kevin Beaumont says a screenshot from it is real. A separate public PoC is also circulating, but its own author now says one of its attack chains is dead and code execution is unreliable. Admins have two stopgaps until the fix lands at 14:00 UTC today. Turning off session.upload_progress.enabled in php.ini disables the feature the leaked details point to. The only cost is upload progress bars. Blocking every request with a multipart Content-Type at the web server goes further, but breaks file uploads
The NCSC is encouraging UK organisations to prepare for immediate updating of systems using PHP. Where immediate remediation is not feasible, organisations should consider taking the system offline until it can be fully mitigated
Widespread internet disruption reported across North Korea. More than 40 websites, including KCNA, Rodong Sinmun and government portals, have experienced significant outages. Network monitors also detected disruptions to Pyongyang's internet infrastructure
The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2. PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence
Multiple online services are down or experiencing issues. Google Cloud has reported "issues" in its western Europe region, affecting dozens of websites, including Revolut, Royal Mail and HSBC
Google Cloud has reported an "issue" affecting dozens of services across the UK They include Revolut, Lloyds, HSBC, Halifax, Rightmove, Royal Mail, Bank of Scotland, DPD and Sky
One week before Serbia's crucial elections, it's confirmed: Belgrade University's rector was hacked with zero-click Pegasus — and a key prosecutor, pulled off a case after speaking out about political interference, got a spyware alert. 16 confirmed targets and counting
Liveuamap is opendata-driven media platform that change the way you receive latest news. Explore a map, messages, pictures and videos from the conflict zones.
If you have a shared mission, or have any questions, just send us an email to [email protected] or contact us on Twitter: @liveuamap
 UkrainaStorskalig brand utbryter vid lager nära Almaz-fabriken i Rostov
 UkrainaStora bränder vid Saratovs oljeraffinaderi efter drönattacker
 California1 killed in south Sacramento crash that left 2 vehicles overturned
 SomaliaTensions are soaring in Beledweyne tonight as heavily armed Macawisley fighters mobilize across the city, sparking fears of an imminent armed clash. The sudden mobilization follows the secretive arrival of a rival Hirshabelle administration deputy leader, who reportedly slipped
 ColoradoDenver Police Arrest Suspect in 2024 Shooting
 VirginiaRichmond police are searching for a hit-and-run driver who struck and killed a man crossing a street in Shockoe Bottom on Friday morning
 IllinoisFatal fire on the 7000 block of N. Paulina yesterday morning, 2-2-2, BC9, E102, T25 joined Pub Ed to distribute smoke detectors & fire safety literature to local residents.
 MinnesotaSaint Paul police officers are currently conducting a death investigation in the 900 block of Mounds Boulevard.
 Iowa2 injured in shooting in Ankeny McDonald's drive-thru