We have noticed that you are using an ad-blocking software
Liveuamap is editorially independent, we don't receive funding from commercial networks, governments or other entities. Our only source of our revenues is advertising.
We respect your choice to block banners, but without them we cannot fund our operation and bring you valuable independent news. Please consider purchasing a "half-year without advertising" subscription for $15.99. Thank you.
Ryska fiskefartyg misstänks för att övervaka viktiga undervattenskommunikationskablar som förbinder Storbritannien med Europa och USA. Över 500 misstänkta rörelser involverande 17 fartyg har identifierats, där fartygen upprepade gånger saktar ner, ändrar kurs och följer kablarnas rutter. Brittiska tjänstemän fruktar att denna aktivitet kan hjälpa Moskva att identifiera mål för framtida sabotage.
Oracle published a security alert for Java today: CVE-2026-91403, CVSS 9.1. It's in JSSE (Java's TLS) and is exploitable over the network without credentials. Affected versions listed: Java SE 8u511, 11.0.33, 17.0.21, 21.0.13, 25.0.5 and 27.0.1, and GraalVM
CRITICAL: GitLab flaw (CVSS 10.0) affects 12 years of releases. CVE-2026-110264 could allow unauthenticated remote code execution on self-managed servers
Microsoft: The China state-aligned threat actor Storm-0940 used the agentic AI penetration testing framework ARTEX to automate attacks targeting hundreds of organizations globally across a broad range of industries. Microsoft Threat Intelligence assesses that Storm-0940 was responsible for the recently disclosed ConnectWise supply chain compromise of a multitenant application. Our investigation found that Storm-0940's use of ARTEX accelerated the speed of compromised application abuse to authenticate to target environments through applications that had already been granted access, allowing the threat actor to operate without requiring an interactive user sign-in. AI-accelerated follow-on activity included reconnaissance, application credential changes, and attempts to modify privileges that could enable expanded or persistent access. Read our blog for a detailed analysis and indicators of compromise (IOCs), along with Microsoft Defender detections, protection recommendations, and guidance on investigating service principal sign-ins and unexpected application credential or privilege changes
Confirmed: Network data show an ongoing disruption to North Korea's already limited internet connectivity. The incident corresponds with the loss of international access to websites under the country's .kp domain
NSA Cyber: Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance
Orange Network Outage: A national outage is affecting Orange and Sosh mobile and internet networks since late morning this Wednesday, October 21. Emergency numbers may be difficult to reach, particularly 15 (SAMU), 17 (police and gendarmerie), and 18 (firefighters). In case of emergency, if your call does not go through, dial 112 from another available mobile network or use a landline
Security firm Calif appears to have a working exploit for the leaked PHP flaws, hours before the patch. A briefly posted video credited to Calif shows it running commands on a WordPress 7.1.3 site on PHP 8.5.4. Kevin Beaumont says a screenshot from it is real. A separate public PoC is also circulating, but its own author now says one of its attack chains is dead and code execution is unreliable. Admins have two stopgaps until the fix lands at 14:00 UTC today. Turning off session.upload_progress.enabled in php.ini disables the feature the leaked details point to. The only cost is upload progress bars. Blocking every request with a multipart Content-Type at the web server goes further, but breaks file uploads
The NCSC is encouraging UK organisations to prepare for immediate updating of systems using PHP. Where immediate remediation is not feasible, organisations should consider taking the system offline until it can be fully mitigated
Widespread internet disruption reported across North Korea. More than 40 websites, including KCNA, Rodong Sinmun and government portals, have experienced significant outages. Network monitors also detected disruptions to Pyongyang's internet infrastructure
The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2. PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence
Multiple online services are down or experiencing issues. Google Cloud has reported "issues" in its western Europe region, affecting dozens of websites, including Revolut, Royal Mail and HSBC
Google Cloud has reported an "issue" affecting dozens of services across the UK They include Revolut, Lloyds, HSBC, Halifax, Rightmove, Royal Mail, Bank of Scotland, DPD and Sky
One week before Serbia's crucial elections, it's confirmed: Belgrade University's rector was hacked with zero-click Pegasus — and a key prosecutor, pulled off a case after speaking out about political interference, got a spyware alert. 16 confirmed targets and counting
Datagroups datacenter i Kyiv har förstörts helt, och det är omöjligt att återställa anläggningen eller fortsätta driften, uppger företagets presstjänst.
Prime Minister Benjamin Netanyahu told Jerusalem_Post that Russia's cooperation with Iran runs counter to its own interests, accusing Moscow of backing antisemitic bot networks targeting Israel
Bekräftat: Den ryska sociala medieplattformen VK (VKontakte) upplever för närvarande en allvarlig störning, med mätningar som visar en anslutning på 56 % av normala nivåer. Incidenten sker samtidigt som det rapporteras om ett ukrainskt drönattacker i närheten av dess datacentrum i St. Petersburg.
Italian airspace experiencing significant disruption today following a "technical anomaly" detected in the geographic data transmission network, according to the country's air traffic control operator ENAV. Operational capacity reduced to 50% of total air traffic, causing delays and cancellations, which will inevitably have a knock-on effect for the entire continent. ENAV has ruled out malicious activity as the cause.
Bulgariska parlamentarikern Ivaylo Mirchev uppger att två personer i masken medvetet satte eld på 11 av 17 Starlink-antenner vid en hemlig anläggning nära Sofia. Antennerna används enligt uppgifter för satellitkommunikation som stödjer Ukrainas krigsansträngning. Bulgariska myndigheter bekräftar att en utredning pågår och att säkerheten vid liknande anläggningar har förstärkts.
Källor inom Ukrainas försvarsministerium bekräftade för Suspilne att begränsningar i Starlink-uppkopplingen upptäcktes under natten inom den ukrainska militären vid hastigheter över 160 km/h. Den exakta hastighetsgränsen kontrolleras fortfarande. Begränsningarna försvårar avsevärt vissa av försvarsstyrkornas operationer, bland annat logistik, obemannade system och attacker på medellångt avstånd. Orsaken utreds.
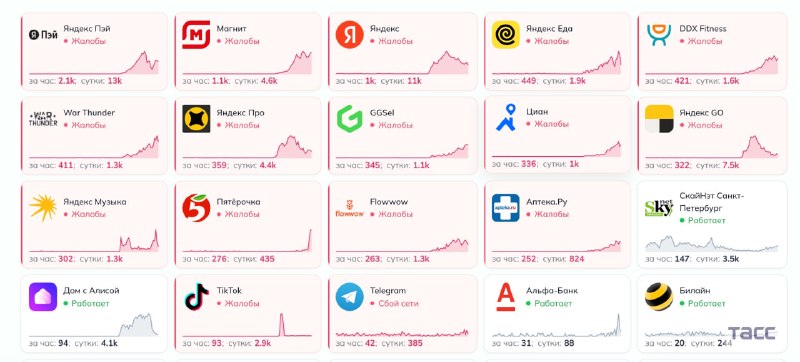
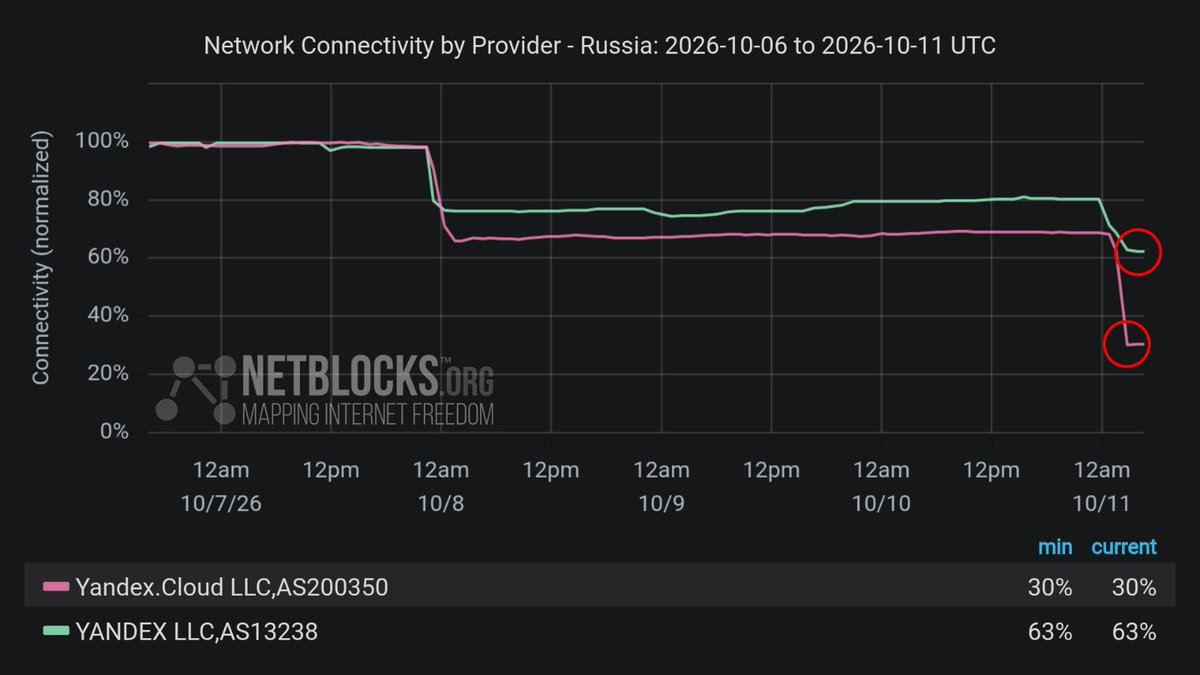
Yandex visar inga tecken på återhämtning under ett långvarigt anslutningsavbrott som enligt uppgifter kan tyda på omfattande infrastrukturskador efter ukrainska drönarattacker mot viktiga datacenter i Sasovo och Vladimir. Den ryska teknikjätten har gett användare i Ryssland och utomlands en dyster prognos.
Ett tredje datacenter tillhörande Yandex har träffats av drönare sedan den 7 oktober. Nätverkstrafiken från Yandex (AS13238) hade redan minskat med cirka 35 % efter attacken mot Sasovo, innan den föll med 99 % jämfört med föregående vecka omkring klockan 00.30 UTC den 11 oktober, då anläggningen i Vladimir enligt företaget stängdes ned.
A cyberattack targeting refrigeration systems at French supermarkets, including Intermarché, Leclerc and Super U, reportedly caused widespread food losses on October 12. Hackers allegedly exploited older software from Danish manufacturer Danfoss to remotely activate continuous defrosting, setting temperatures as high as 50°C and destroying fresh and frozen products. Around 150 Intermarché stores were reportedly affected, alongside Leclerc, Super U and potentially other retailers. Two supermarkets in Alsace reported combined losses of €270,000, while nationwide damage could reach several million euros
Multiple users report internet access has been throttled in Azerbaijan. Main apps appear to be Instagram, TikTok and other social media where you can share videos
Bekräftat: Mätningar visar en andra kollaps i nätverken för den ryska teknikjätten Yandex efter en ny ukrainsk drönattacker mot datacentraler i Vladimir i morse. Kampanjen kommer kort efter Rysslands hot om att ge Ukraina en "digital detox".
Liveuamap is opendata-driven media platform that change the way you receive latest news. Explore a map, messages, pictures and videos from the conflict zones.
If you have a shared mission, or have any questions, just send us an email to [email protected] or contact us on Twitter: @liveuamap
 YemenHouthi-held Hodeidah airport, telecommunication networks on Mount Bard in Kusmah district, Raymah governorate and in Bani Matar in Sana'a were targeted by airstrikes. Photo from Hodeidah airport